
From Binance to PHP2Shell: Redefining the Frontline of Web Security in the AI Era

 Prefer us on Google


Attackers are penetrating the entire trust chain, and Vitalik's d/acc is also trying to redirect the technological acceleration towards defense.
On the morning of October 30, the crypto market experienced yet another historic theft incident, this time involving Binance.
According to preliminary investigations, the attackers may have gained access to a service container by hacking into a DevOps engineer's laptop and submitted unauthorized withdrawal transactions. Binance estimates the total impact of the incident to be as high as $6.3 billion, and approximately $3 billion in related assets have already been frozen in collaboration with authorities.
Over the past year, security incidents at major exchanges have become increasingly frequent:
Last year, Bybit suffered a theft of approximately $1.46 billion in assets, and in September this year, Bitget experienced an unauthorized transfer of about $387.5 million in assets. Now, Binance has also found itself embroiled in a new crisis.
When observing recent security incidents together, a clear trend emerges: attackers are increasingly avoiding direct brute-force attacks on cryptography and private keys, instead focusing on the entire 'trust chain'—from employee terminals and third-party security products to software supply chains, service containers, and transaction authorization processes. Any crack in one link can lead to the collapse of the entire defense line.
The rapid development of AI is further amplifying these risks.
On October 22, Ethereum co-founder Vitalik Buterin proposed a new judgment: In the AI era, the ultimate outcome of cybersecurity may favor defenders, but the transition period to this outcome will be extremely difficult.
1. From Bybit to PHP2Shell: Attackers are Penetrating the Entire Trust Chain
Let’s review these incidents.
Their attack paths differ, but they share a common point: attackers did not simply rely on cracking private keys or breaching the underlying blockchain protocols; instead, they found a default trusted link within the system.
- In the Bybit incident, attackers used social engineering to infiltrate a developer's device at Safe, obtaining relevant access credentials and subsequently controlling the front-end resources within the Safe wallet infrastructure;
- In the Bitget incident, attackers exploited vulnerabilities in third-party security products to gain internal high-privilege credentials, then bypassed existing risk control mechanisms with forged withdrawal instructions;
- In the latest Binance incident, the attack path likely began with the invasion of a DevOps engineer's laptop;
These three incidents involved third-party wallet infrastructure, third-party security products, and internal development and operations environments, respectively.
This explains why traditional cold wallets and multi-signature mechanisms cannot solve all problems; after all, what attackers truly exploit are those trust links that can influence the final execution of transactions but have not been independently verified.
Similar trust chain crises do not only exist in crypto exchanges.
Just a week before Binance was attacked, Binance founder CZ specifically tweeted, reminding everyone to be extra cautious when visiting any website in the coming days—at that time, two epic high-risk vulnerabilities in the PHP core engine (CVE-2026-109618 and CVE-2026-109619, with a CVSS v4.0 score of 9.2) were causing panic across the internet.
As an open-source server-side language that supports about 70% of websites globally, major platforms like WordPress, Magento, and Drupal are all built on PHP.
These two vulnerabilities, which have been lurking for over a decade in memory management and global state reset, allow attackers to achieve remote code execution (RCE) without authentication, simply through a specific web request, taking over servers and implanting backdoors or stealing user credentials before the website's application code runs.
Network security agencies Palo Alto Networks and Censys have scanned and found that over 22.6 million to 36.7 million exposed instances worldwide are at risk.
Even more outrageous, according to security agencies, these two long-dormant, hard-to-detect underlying memory state vulnerabilities were discovered using AI technology, in other words, AI has significantly lowered the threshold for turning hidden underlying logical flaws into usable attack payloads.
We have previously discussed the three major qualitative changes in network attack methods in the AI era (further reading: "How will the arms race of 'spear and shield' in Web3 upgrade when hackers become 'more efficient' with AI?"):
- 'Industrialization' of zero-day vulnerability (0-day) mining: In the past, finding deep memory vulnerabilities in PHP core engines or firmware layers required top security experts to spend months on manual code audits and fuzz testing. Now, AI can scan global open-source code repositories around the clock at a very low cost, turning decade-old bugs into deadly weapons in bulk;
- Extreme compression of 'patch time windows' (N-day): Once vulnerability information is leaked or patch code is submitted, malicious attackers can use AI to reverse-engineer the patch, automatically generate variant exploits, and complete automated scanning and injection across the network in minutes. The upgrade schedules that traditional operations teams calculate in days or weeks become meaningless in the face of AI attack scripts that respond in milliseconds;
- Software supply chains and DevOps become the number one breakthrough point: Modern Web3 and financial systems are not built in a vacuum; front-end interactions, back-end containers, third-party NPM/PyPI dependency packages, and engineers' local development environments constitute an extremely large and fragile open-source supply chain;
Just as Binance's DevOps container was infiltrated and Bybit faced front-end supply chain tampering, the crypto industry is experiencing a wave of 'global AI hacker attacks at a pandemic level' because on-chain attacks are the easiest to monetize.
Of course, not all of the aforementioned attacks are directly initiated or executed by AI, but AI is simultaneously amplifying the capabilities of both attackers and defenders, and under the existing software engineering system, this amplification effect exacerbates the structural asymmetry that already exists between the two sides.
2. Vitalik: The Endgame May Favor Defenders, but the 'Transition Period' Will Be Incredibly Difficult
In response to the industry discussions triggered by AI uncovering underlying vulnerabilities like PHP2Shell, Vitalik Buterin provided a very calm judgment on October 22: The long-term endgame of cybersecurity may form a pattern favorable to defenders, but the transition period will be extremely difficult.
Why?
Because under the current software engineering paradigm, there is a natural asymmetry between attackers and defenders. A large software system may contain millions of lines of historical code, hundreds of external dependencies, and numerous complex permissions and execution paths.
Defenders must ensure that all critical links are sufficiently secure, while attackers only need to find one undiscovered gap.
Vitalik specifically pointed out that merely relying on security researchers to discover vulnerabilities in published software before hackers does not truly establish a defensive advantage, because if both sides use increasingly powerful AI, it essentially becomes a competition of who can find vulnerabilities faster.
What truly needs to change is the way software is constructed, such as the two core directions he proposed: formal verification and minimizing the trusted computing base (TCB).
First is formal verification, which aims to replace 'experience debugging' with mathematical proof.
Traditional software testing can only prove 'no bugs were found in tested scenarios,' but can never prove 'the code is absolutely bug-free.' Formal verification uses rigorous mathematical logic to prove that a piece of program code strictly meets expected security specifications under all possible inputs and state transitions, without memory overflow, state not reset (like PHP2Shell), or logical reentrancy defects.
In the past, the cost of formal verification was extremely high, and the amount of code required to write mathematical proofs was often several times that of business code, only aerospace or core cryptographic protocols could afford it.
But in the AI era, AI can not only find vulnerabilities but also become a super assistant in writing formal verification proofs. Therefore, Vitalik predicts that in the future, 'AI-assisted formal verification' will become the ultimate form of software development—whether it is encryption communication protocols like Signal, TLS, ZK-EVM, or application layer smart contracts, all can automatically generate end-to-end mathematical security proofs through AI before code release.
When a piece of code is mathematically proven to be 'flawless,' even the strongest AI capabilities of attackers cannot find non-existent vulnerabilities.
Secondly, minimizing the trusted computing base (TCB) aims to compress the attack surface to the extreme.
What is the trusted computing base (TCB)? In simple terms, it is the totality of all hardware and software components that a system must unconditionally trust to ensure security and that will not fail.
Looking back at Binance's $6.3 billion security incident and Bybit's multi-signature hijacking incident: why were the underlying private key algorithms intact, yet assets were lost? Because their TCB was too large—massive container clusters, complex operational permission pipelines, the operating systems of developers' laptops, and the JavaScript libraries rendered on the front end were all included in the trust chain that could lead to fund loss once breached.
The core idea of TCB minimization is to do subtraction and isolation: consolidate the functions that truly involve private key protection, signature verification, and core authorization into a smaller scale, more clearly defined, and auditable secure environment, while other complex functions should run in a restricted peripheral environment as much as possible.
Even if browsers, plugins, front-end services, or AI agents are attacked, they should not be able to gain unrestricted access to manipulate user assets directly.
From this perspective, this is also the value of non-custodial wallets like imToken. When using centralized exchanges, user assets need to go through platform accounts, custodial wallets, and internal withdrawal systems; whereas with imToken, users manage their private keys themselves, directly control their on-chain assets, and initiate transactions, reducing the intermediary step of centralized custody.
A shorter trust chain means less exposure to platform-level risks, and users do not have to worry about exchanges suspending withdrawals or freezing platform account balances. Of course, users also need to take responsibility for the security of their private keys and devices.
III. From Technical Acceleration to Defensive Accelerationism: Why Do We Need d/acc?
If formal verification and TCB minimization answer the question of "how to be safer technically," then Vitalik's long-advocated d/acc attempts to address a more macro question:
As AI and other cutting-edge technologies rapidly change the world, how should we prioritize technological development?
d/acc, short for Defensive Accelerationism, is often referred to as "defensive accelerationism." Vitalik systematically proposed this concept for the first time in 2023 and further elaborated on it in 2025's "d/acc: one year later."
It does not oppose technological progress but emphasizes a selective acceleration: prioritizing the development of technologies that can enhance social defense capabilities, decentralize power, and reduce systemic risks.
Compared to the comprehensive acceleration emphasized by e/acc, d/acc focuses more on whether technology enhances offensive capabilities or improves defensive capabilities (for further reading, see "When Web3 Meets d/acc: What Can Crypto Do in the Era of Technological Acceleration?").
In the vision of d/acc, this defensive system encompasses four dimensions of in-depth construction:
- Network Defense: Reducing the success rate of cyber attacks and protecting digital assets and data through cryptography, formal verification, software isolation, and vulnerability detection;
- Biological Defense: Enhancing society's ability to respond to biological security risks through pathogen detection, air monitoring, vaccine development, and public health technologies;
- Physical Defense: Reducing the vulnerability of critical real-world facilities to attacks through distributed energy, resilient communication networks, and infrastructure resilience construction;
- Information Defense: Countering misinformation, deepfakes, and large-scale information manipulation through privacy protection, information source verification, and decentralized collaboration mechanisms;
These areas may seem vastly different, but they all revolve around a common goal: while technology continuously enhances the capabilities of individuals and organizations, it also enables them to acquire matching self-protection capabilities, preventing more powerful technologies from being concentrated solely in the hands of a few with resources and control.
It was also during the discussion of the PHP vulnerability incident that Vitalik reiterated a hardcore assertion within the d/acc framework—facing the asymmetric impacts brought by cutting-edge AI, high-risk aggressive AI's chaotic advancement should be approached cautiously at necessary stages; at the same time, society should systematically invest more than 1% of GDP resources into cybersecurity, biological security, and physical world security reinforcement.
Why is such large-scale systematic investment necessary?
Because the benefits brought by technological progress can often be quickly priced and commercialized by the market, but the value of security infrastructure is frequently underestimated.
Companies are willing to invest huge sums for more powerful AI models, faster computing power, and more efficient software development tools, but may not be willing to provide equivalent support for the long-term maintenance of underlying open-source software, formal verification, and security audits. If this resource mismatch is not proactively corrected, the digital towers built on fragile open-source foundations will only become increasingly dangerous.
-- Price
Conclusion
From the global internet infrastructure risks exposed by PHP2Shell to the major security incidents occurring in Bybit, Bitget, and Binance, the cybersecurity situation in 2026 is reminding everyone with real monetary costs:
The offensive and defensive competition in the AI era is no longer just about who can discover vulnerabilities faster, but whether the entire software ecosystem can establish a sufficiently reliable defense system.
Security can never be a one-time effort, but that does not mean it is an unwinnable war of attrition.
Over the past few decades, cryptography has proven that certain defensive capabilities can be established with very strong security guarantees through mathematical principles, rather than solely relying on defenders investing more manpower.
The combination of AI with formal verification, minimal trusted computing bases, and other technologies also has the opportunity to further extend this concept to the entire software system.
For ordinary users, this security concept can also be implemented in the choice of asset management methods.
Choosing a non-custodial wallet like imToken essentially means keeping control of assets in one's own hands, reducing reliance on centralized platform custody and internal operational systems. Of course, this also means users need to pay more attention to mnemonic phrase management, device security, and authorizing each transaction. But at least, whether assets can be controlled by oneself no longer completely depends on whether a centralized platform operates normally.
Perhaps this is the true meaning of what Vitalik said about the potential for a favorable outcome for defenders in network security: not to expect that one day AI will no longer find any vulnerabilities, but to steadily ensure that the critical systems we rely on can continue to operate reliably, even in the face of increasingly intelligent attackers, by relying on smaller trusted cores, stricter permission boundaries, and more verifiable security mechanisms.
Technological progress deserves acceleration, but the ability to protect technological achievements and individual assets also needs to be accelerated.
This content is provided for general informational purposes only and doesn't constitute financial, investment, legal, or tax advice. Any events, rewards, online promotions, or related information mentioned herein should not be considered a recommendation, solicitation, or invitation to purchase, sell, trade, or otherwise deal in any crypto assets. Crypto assets are highly volatile and may result in loss. The availability of WEEX services, products, and related events may vary by region. You are responsible for ensuring that your participation is in accordance with applicable local laws and regulations.
You may also like
Anonymous Interviews with Frontline Investors and Entrepreneurs: Who is Forcing Whom to Chase Consensus?
Google DeepMind Research Claims AI Collaboration Ability is Key to Economic Transformation
Google Cloud Previews Institutional Crypto Key-Security Service as Custody Risks Grow

Coinbase CEO Plans to Sell 8.1674 Million Shares Worth Approximately $1.31 Billion
$470 billion wiped out, Wall Street plunges amid inflation
Solana's Tokenized Asset Value Exceeds $5.19 Billion
Crowded, Confused, and Missing the Boat: Multiple Extreme Signals Emerge in Global Markets
Collector Crypt CEO: The Real Threshold of Digital Card Drawing Platforms Lies in These Four Aspects
When will the next crypto bull run happen?
Midterm Election Predictions: Why Use Four Contracts to Measure Senate Control?
Why is Strive More Aggressive than Strategy in Financing Bitcoin?
Morpho RWA deposits pass $2B as loans approach $900 million
Key Institutional Prerequisite for Tokenization: Issuer Authorization
Kalshi Discusses User Protection Measures with Regulators, Willing to Raise Participation Age to 21
A New Wave of TGE? 19 Projects Expected to Launch Intensively in Q4
OCC Finalizes Stablecoin Issuance Guidelines in the U.S.
Reviewing the US, India, and South Korea: How Retail Investors Ignite the Options Market?
Looking Ahead to Tonight's Federal Reserve Meeting: A Pause in Rate Hikes in October is Almost Certain, How It Affects December Rate Hike Probabilities Becomes the Focus
On-Chain Options Blue Ocean: The Real Battlefield is in Retail Distribution
Robinhood Predicts Market Gains, But Crypto Revenue Halves
Bitcoin: Small Holders Leave, Big Buyers Step In
Bitcoin: Hyperliquid Whales Go Short for the First Time Since March
Why JPMorgan Raised the Target Price for Yushu Technology to 995 Yuan
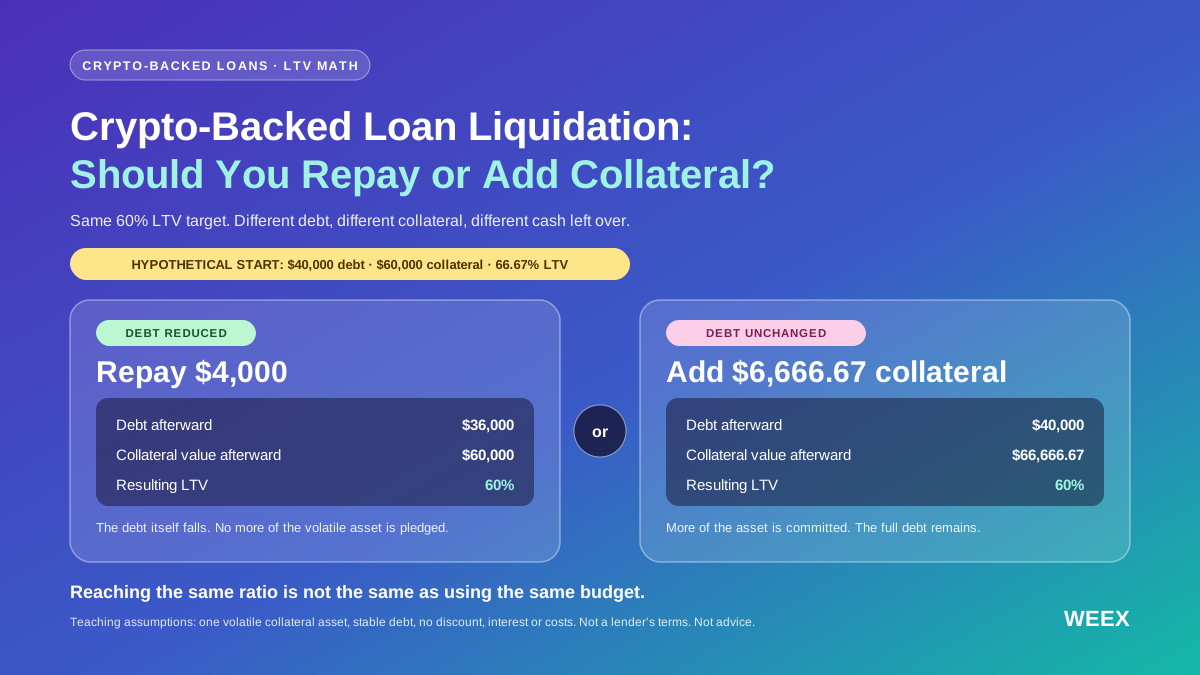
Crypto-Backed Loan Liquidation: Should You Repay or Add Collateral?
Facing crypto-backed loan liquidation? Compare repayment and collateral top-ups using equal budgets, LTV calculations, stress tests and protection limits.
Turbulent Middle Eastern Crypto Market Welcomes Leadership Change
Ritual Raises $30 Million to Launch Token: AI Game Changer or Retail Investor Trap?
Global Markets in the Last 24 Hours: Brent Oil Reaches $115.81, Bitcoin Drops to $79,818
The Mismatch Between Capital Frenzy and Deployment Economics in the Embodied Industry Clock Cycle
One Week Countdown to Midterm Elections! Will Crypto Change?
Bitcoin at $90,000: The $68 Million Bet on the U.S. Midterm Elections
Anonymous Interviews with Frontline Investors and Entrepreneurs: Who is Forcing Whom to Chase Consensus?
Google DeepMind Research Claims AI Collaboration Ability is Key to Economic Transformation
Google Cloud Previews Institutional Crypto Key-Security Service as Custody Risks Grow
Coinbase CEO Plans to Sell 8.1674 Million Shares Worth Approximately $1.31 Billion
$470 billion wiped out, Wall Street plunges amid inflation
Solana's Tokenized Asset Value Exceeds $5.19 Billion
Contents
Latest articles


Latest coin listings on WEEX


