
Security Researcher Exploits PHP2Shell Vulnerability to Breach Bounty Website, Earns Approximately $2000 in Bitcoin Rewards

 Prefer us on Google


Security researcher killa successfully exploited the PHP2Shell vulnerability to breach the bounty website stealmybitcoin.com, claiming a Bitcoin reward valued at approximately $2021 (0.02511679 BTC). The vulnerability (CVE-2026-109618 and CVE-2026-109619) was disclosed on October 20, and due to the delayed appearance of the attack code, the website was set up on October 24 using an unpatched version of PHP, offering a bounty of about $500 in Bitcoin to verify the vulnerability. The reward later increased to around $2000 due to donations. Approximately 19.5 hours after the challenge began, killa wrote usable attack code and successfully retrieved the private key from the server. The website creator confirmed that the challenge was resolved, acknowledged the success of the attack, and pointed out that there was an error in placing the key. Killa subsequently published the complete PoC on GitHub.
-- Price
This content is provided for general informational purposes only and doesn't constitute financial, investment, legal, or tax advice. Any events, rewards, online promotions, or related information mentioned herein should not be considered a recommendation, solicitation, or invitation to purchase, sell, trade, or otherwise deal in any crypto assets. Crypto assets are highly volatile and may result in loss. The availability of WEEX services, products, and related events may vary by region. You are responsible for ensuring that your participation is in accordance with applicable local laws and regulations.
You may also like
Circle launches cirBTC for Ethereum and Arc with unified balance
Anthony Pompliano: The State Will Never Stop Printing Money! Bitcoin, Gold, and Land Will Benefit for 20 Years
Ansem is Bearish on Bitcoin and Ethereum, Market May Correct Before Rising
Leon Wankum Predicts Bitcoin Will Outgrow Real Estate Market
Blockstream Executive Peter Bain: Bitcoin Holding $81K Signals Bull Run
Bitcoin-to-Nasdaq Ratio Turns Bullish After 235 Sessions
PHP Exploit Takes Down Government and Hospital Websites
Galaxy Believes Bitcoin Bear Market Ended in June, Recommends Buying and Holding
Empery Invests $65 Million to Acquire 25% Stake in AI Data Center
Bitcoin's next Fed test comes with a hidden problem in America's inflation data
The crypto market loses altitude, patience becomes a habit – Steady Lads
Bitcoin's flat trend vs. S&P 500 signals risk warning, says Bloomberg analyst
Cyberattack on GMO in Japan: Trading Accounts Compromised, GMO Coin Claims to be Unaffected

Mark Cuban compares Bitcoin to meme stocks
Electrum patches Bitcoin vulnerability allowing payment redirection
The Week Ahead: 4 Key Moments for the Crypto Market
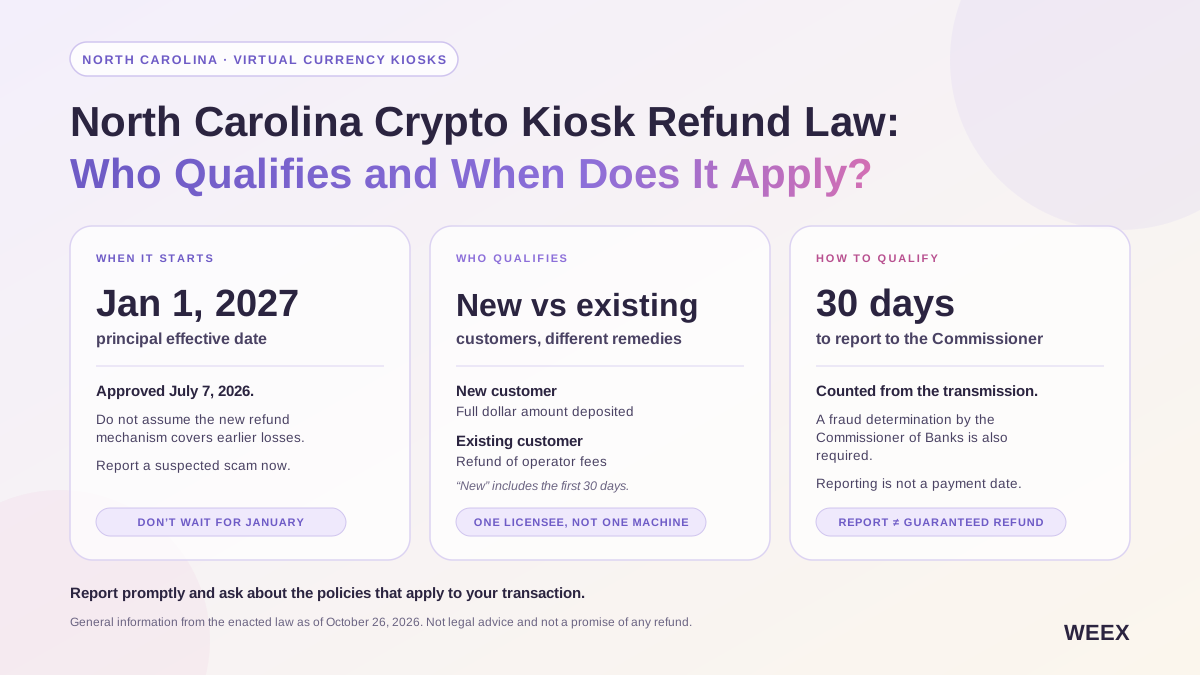
North Carolina Crypto Kiosk Refund Law: Who Qualifies and When Does It Apply?
Understand North Carolina’s crypto kiosk refund law: the January 2027 start date, who qualifies, reporting deadlines, and documents victims should keep.
US Startup Successfully Develops Artificial Gold, Highlighting Bitcoin Scarcity
Sam Price Claims Bitcoin Has Been Declared Dead Multiple Times
Mr&强 Analyzes Bitcoin Support and Resistance Areas
Franklin Templeton Launches Two Dividend Reinvestment Bitcoin ETFs
Interest on U.S. corporate bonds with CCC rating rises to 17.99 percent
LND Releases v0.21.5-beta.rc1 with Fee Estimate Limits
FOUNDATION Faces Spam Attack from Spoofed Domain Names
Bitcoin Core Changes Rules for Disclosing Security Vulnerabilities
New York Man Sentenced to 51 Months in Prison for Telecom Fraud and Money Laundering
[Bitcoin $0 Controversy②] "$0 is an Exaggeration"... Reasons Wall Street Disagrees
WEEX Exclusive:Gold Breaks Below $4,000, Bitcoin Pulls Back Below $80,000 | WEEX TradFi Daily(October 26, 2026)
Gold Breaks Below $4,000, Bitcoin Pulls Back Below $80,000 | WEEX TradFi Daily(October 26, 2026)
At the October 23 close, major indexes were mixed, with the Dow weaker. Brent crude rose to about $116.7, a near six-month high, and energy led; gold briefly fell below $4,000 as Bitcoin pulled back toward $80,000. Cybersecurity stocks strengthened last week, with CrowdStrike up nearly 12%. Markets are watching whether Bitcoin’s correction is nearing its end, along with earnings from Verizon, Cadence, Celestica and Amkor today.
The Superintendency of the Securities Market of Panama Excludes Cryptocurrencies from Its Oversight
Circle launches cirBTC for Ethereum and Arc with unified balance
Anthony Pompliano: The State Will Never Stop Printing Money! Bitcoin, Gold, and Land Will Benefit for 20 Years
Ansem is Bearish on Bitcoin and Ethereum, Market May Correct Before Rising
Leon Wankum Predicts Bitcoin Will Outgrow Real Estate Market
Blockstream Executive Peter Bain: Bitcoin Holding $81K Signals Bull Run
Bitcoin-to-Nasdaq Ratio Turns Bullish After 235 Sessions
Contents
Latest articles



Latest coin listings on WEEX


